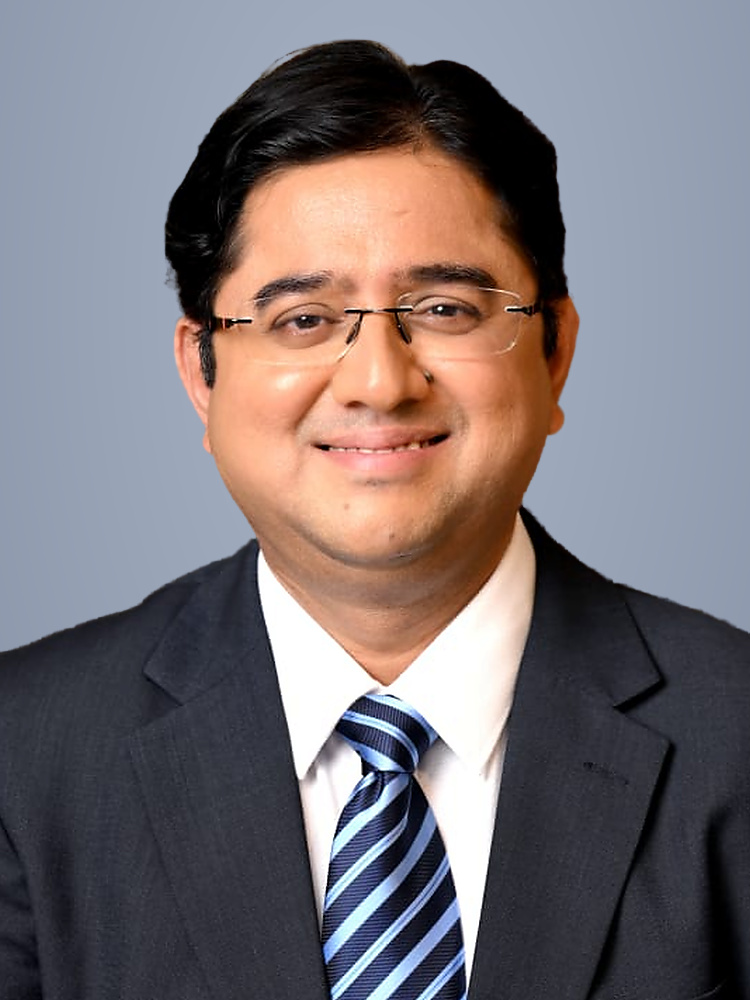
Vishal Samant
CDO & CISO
A seasoned technology leader with nearly 20 years of experience across IT strategy, project management, IT operations, solution architecture, digital transformation and database administration, with extensive exposure to the financial services and asset management industry. Prior experience includes senior leadership roles at The Wealth Company, where he served as Chief Technology Officer, and at Aquila I, Mirae Asset Investment Managers, Mirae Asset Global Investments, IDFC Asset Management Company and ICICI Prudential Asset Management Company. He has led initiatives across IT infrastructure, information security, application support, project management and enterprise-wide digital transformation. The overall experience reflects a strong focus on secure and scalable technology platforms, regulatory alignment and an enhanced investor and stakeholder experience. Vishal holds an MBA in Information Management from TIMSR and has completed the eMDP Professional Certificate Program – Strategy in the Digital Age from IIM Kozhikode. He is also an Oracle Certified Professional and ITIL V3 certified. In the current role, he will be responsible for overseeing the digital strategy, technology governance and information and cyber security function at Carnelian Mutual Fund, with a focus on resilience, efficiency and service quality.
Roles and Responsibilities for Risk Management
- Adherence to the guidelines pertinent to SEBI in respect of RMF and the SEBI Cybersecurity and Cyber Resilience Framework (CSCRF), including risk identification, risk management, risk reporting (both periodic and escalation of material incidents) and corrective actions taken.
- Defining specific responsibility regarding risk management of key personnel reporting to them.
- Maintaining risk levels as per the risk metric.
- Implementation and periodic review of the information security policy, cyber crisis management plan, and business continuity and disaster recovery arrangements.
- Timely reporting of cyber incidents and material technology disruptions to the regulator and the relevant internal committees, as applicable.
- The CDO & CISO shall take immediate corrective action for non-compliance or major findings, post approval from CEO as per DoP, and shall report to CRO regarding the risk reports.
- The CDO & CISO shall escalate to CEO and the CRO any major findings reported by the respective risk management function.